Which assurance route covers this work
Print-side data handling is governed by the PDPA and by the terms of the engagement, not by the ABS OSPAR audit. Our OSPAR-audited scope is mailroom, messaging and local courier services, and it does not extend to printing or lettershopping — we set that out in full on our page explaining what it means to be OSPAR audited. For the print side, the PDPA is the operative framework, and its obligations on a data intermediary carry financial penalties, so it is not the weaker route. It is the applicable one.
Which obligations sit with us, and which stay with you
Section 4(2) of the PDPA applies the Protection Obligation and the Retention Obligation, sections 24 and 25, to a data intermediary processing data under contract. Consent, notification, access and correction are not carved in: those remain with the organisation that collected the data. Section 4(3) then puts it beyond doubt from the other direction, giving the sending organisation the same obligation for data processed on its behalf as if it had processed the data itself. Nothing you send us reduces what the PDPA asks of you. What it does is add a second party who is answerable for the production controls.
What PDPC asks of a print vendor
PDPC's printing guide is advisory rather than binding, and it names the controls it expects to see. The roles of do-er and checker should be separated so the check is independent. The checker should be trained in the method of checking. There should be a documentary trail of both. Checks should be proportionate to the volume and sensitivity of the data, and placed at a stage where a correction can still reverse the error rather than record it. We work to that structure, and it is worth reading the guide before you write your next print tender, because it is also the clearest statement of what you are entitled to ask for.
Why a re-sort invalidates the check before it
In Aviva Ltd and Toh-Shi Printing Singapore Pte Ltd [2016] SGPDPC 15, statements for 7,794 policyholders went out carrying the wrong information, disclosing the personal data of 8,022 individuals. The client had signed off sample cases before printing. The vendor then sorted the data again, by postal code, overseas address and undeliverable mail, and printed on the strength of the earlier sign-off. The Commission found the breach would have been prevented had the vendor issued fresh samples after that sort and re-run its quality checks against the client's original source data. The operating rule we take from it: any step that reorders or re-associates a file invalidates the check that came before it, so the check runs again, against source, not against the intermediate file.
Encrypted transfer
Data should never move by ordinary email. Files travel over SFTP with AES-256 encryption, which keeps them unreadable to anyone intercepting them in transit. PDPC's printing guide names SFTP among the measures it lists for protecting personal data on its way to a print vendor, alongside password protection and encrypting portable media.
Restricted-access processing
While a job is running, the live customer file is open to the people running it rather than to the wider business, and for the duration of the job rather than indefinitely.
Purge after production
Section 25 asks an organisation to stop retaining personal data once the purpose it was collected for is no longer served and retention is no longer needed for legal or business reasons. In print work that point arrives early, usually at lodgement. Data is removed after production rather than held on a production server, and we will tell you when that happened for your job. PDPC's guide suggests specifying a deletion period and keeping a retention schedule rather than relying on an assurance, so ask for the period in writing.
Recipient matching and window checks
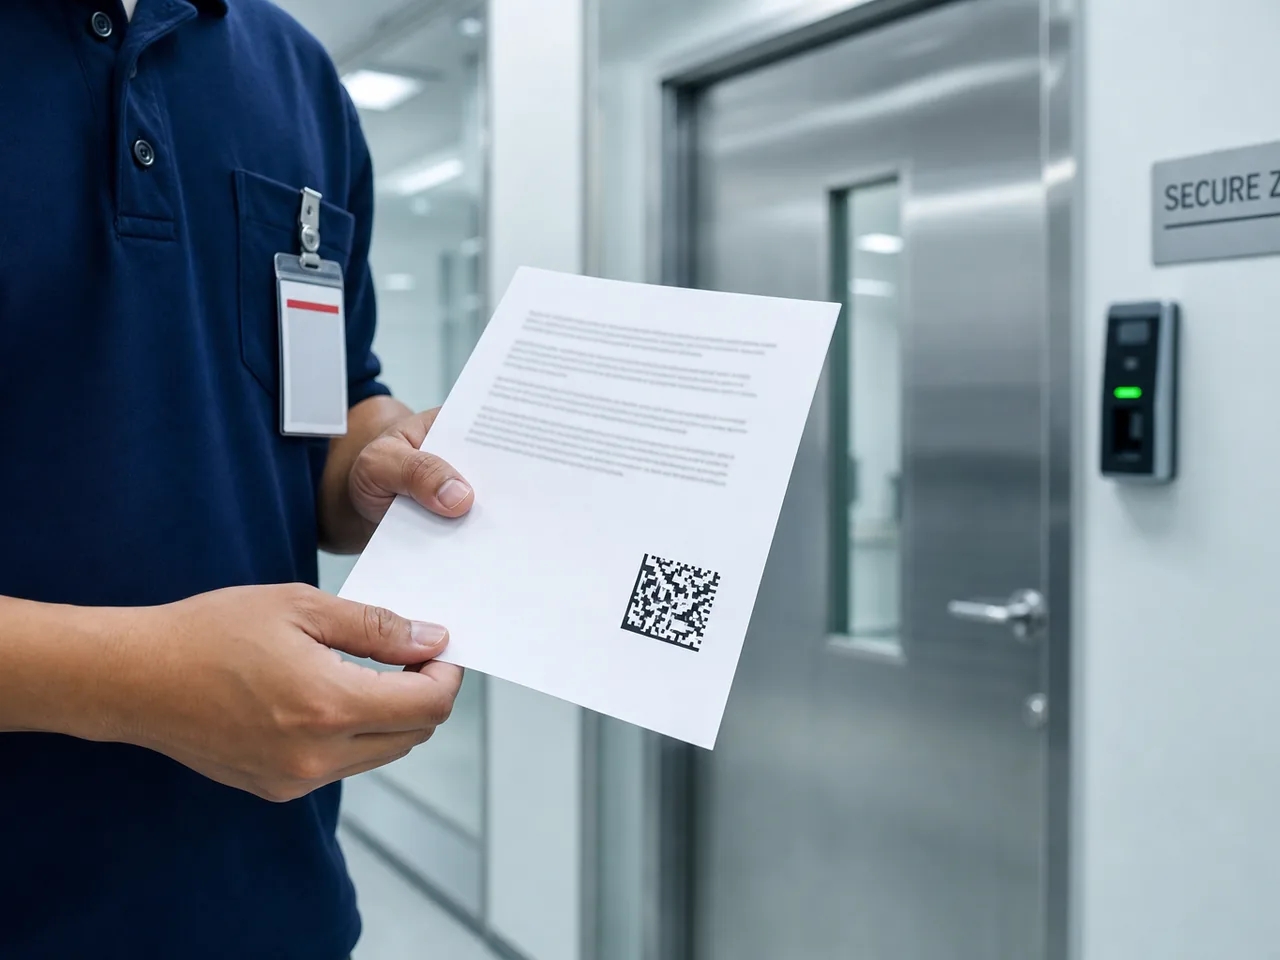
The characteristic failure in mail production is one recipient receiving another recipient's document. A 2D barcode on the page is matched against the envelope before sealing, so a mismatch halts the pack rather than being sealed and lodged. Where an envelope has a window, the position of personal identifiers on the page decides what is visible from outside, so page layout is checked against the window as a privacy control rather than a print-quality one.
Records you can produce afterwards
Production steps are logged and reconcilable against your input file, so you can show what was produced, how many pieces, and when they were lodged. For regulated senders this is usually the part that matters most, because an assurance conversation turns on what you can evidence after the fact rather than on what was intended.